
Last updated: August 28, 2026
Key Takeaways for OnlyFans AI Agencies
- AI-generated content increases revenue for OnlyFans agencies but also increases ban risk when compliance breaks across multi-creator teams.
- A 7-step pre-upload checklist connects identity checks, likeness rights, workspace isolation, and audit trails to concrete production actions.
- EU AI Act Article 50 transparency duties start 2 August 2026 and require digitally-signed metadata plus imperceptible watermarking during generation.
- Manual disclosure and platform tagging fail at agency scale; verification inside the creation tool is the only scalable way to create audit trails.
- Sozee builds these controls into every workflow so compliance becomes structural, not a separate task get started with Sozee today.
The Problem: Why Multi-Creator AI Teams Lose Accounts
The gap between written AI policy and real team behavior is now systemic. A 2026 vendor-run survey of roughly 300 creative professionals found that 96% of organizations have formal AI usage restrictions while 96% of employees in those same organizations admit using unapproved AI tools, which creates a near-perfect compliance failure rate. For OnlyFans agencies that manage multiple creator accounts at once, that gap becomes a direct and ongoing revenue risk.
Risk grows as teams grow. Data-privacy concerns with AI-generated work are widely reported among companies, and agencies running creator rosters sit in the highest-risk group. An independent 2026 study of nearly 1,800 creative professionals across more than 60 countries found that 58% had used AI in client work without disclosing it, and only about one-third said they always disclose AI use to clients.
Platform enforcement patterns confirm this risk. Account restriction risk increases when teams operate without clear account ownership, shared sessions, consistent operator behavior, strong recovery logs, or pause-and-review rules in multi-account operations. AI content that lacks disclosure metadata, synthetic-identity documentation, or workspace isolation sends exactly the signals that enforcement systems are trained to flag.
The EU AI Act adds a regulatory layer for any agency distributing content into European markets. Article 50 transparency duties apply from 2 August 2026, with a grace period until 2 December 2026 only for the marking obligation on generative AI systems placed on the market before that date. The voluntary Code of Practice offers one compliance path through digitally-signed metadata and imperceptible watermarking.
The Solution: 7-Step Pre-Upload Compliance Checklist
The risks above share a common cause: broken workflows rather than missing knowledge. This checklist addresses those risks by baking compliance checks into production so every asset meets platform, legal, and regulatory rules before upload.
The following checklist maps each step to a specific compliance control. Complete steps 1 through 7 in sequence for every asset before upload.
- Verify the account identity and AI-character registration against platform requirements.
- Confirm likeness-ownership documentation is current and on file.
- Log the reusable asset record for every setting, outfit, and object used in the shoot.
- Confirm workspace isolation so each creator character operates in a fully separated environment.
- Apply SFW-to-NSFW ramp controls and confirm the content ceiling matches the account tier.
- Run an agent-assisted shoot audit trail and verify the log is complete before upload.
- Execute post-upload monitoring and document rollback steps in case of enforcement action.
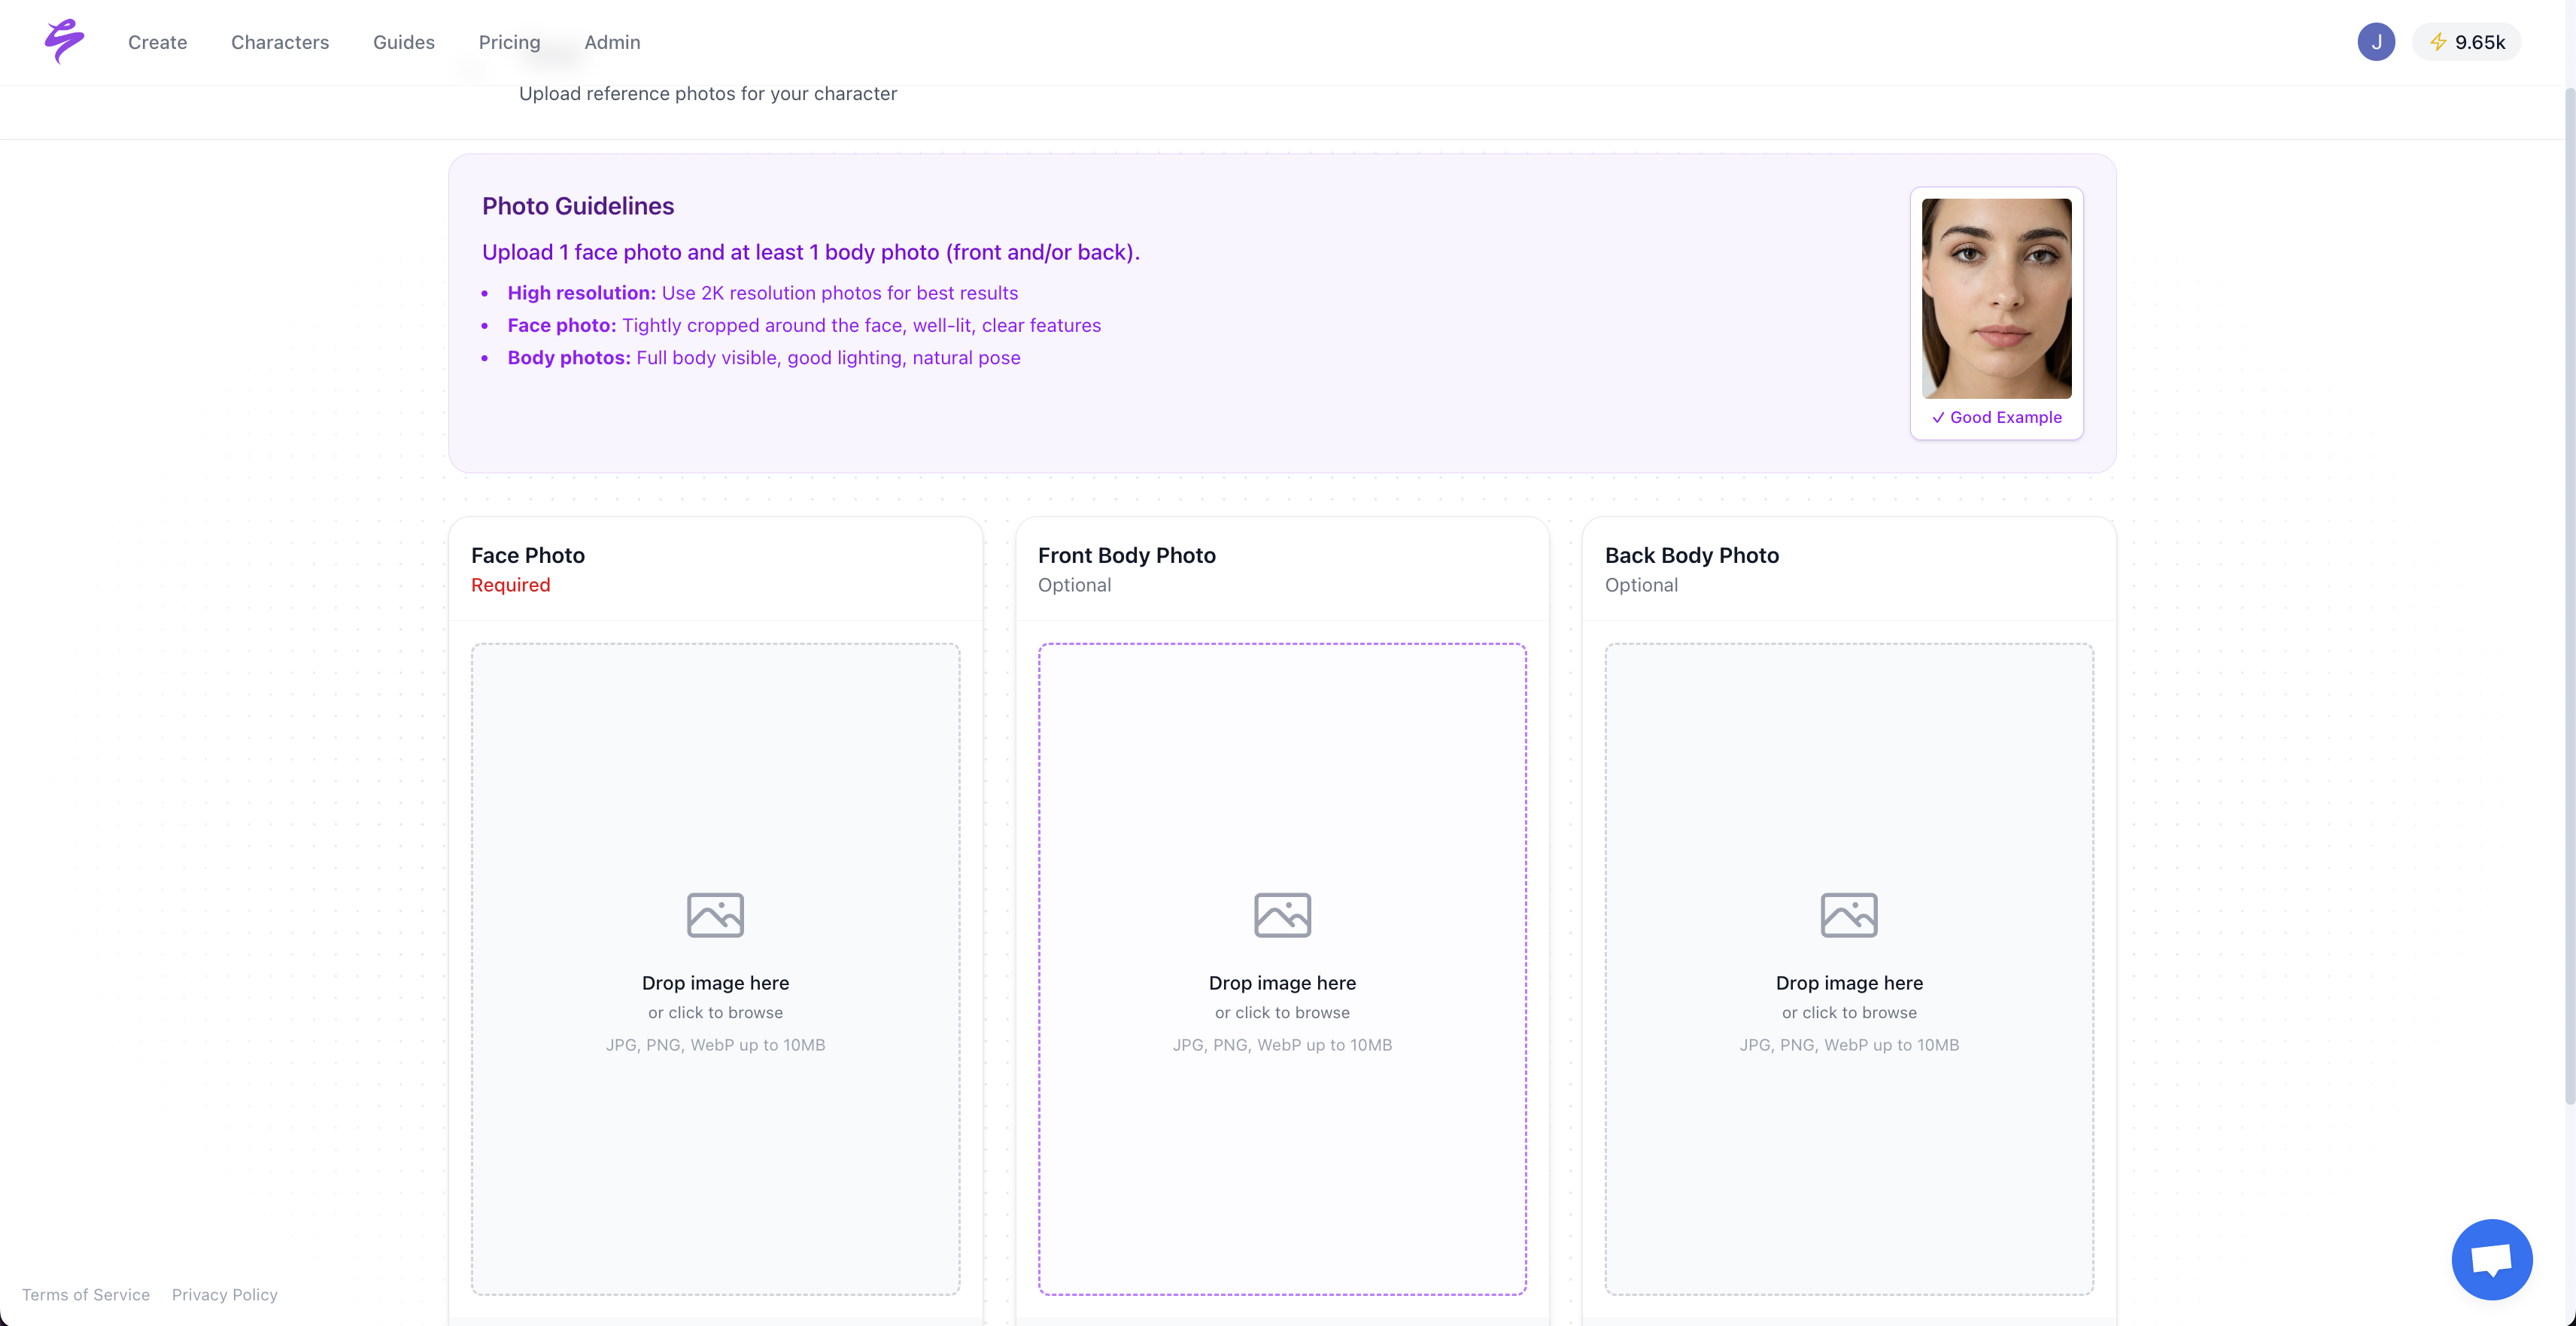
Verified-Account and AI-Character Setup
Sub-Checklist for Account and Character Setup
- Confirm the OnlyFans account has completed platform identity verification before any AI content goes live.
- Register each AI character as a distinct entity within the account, with a named human owner of record.
- Document whether the character is based on a real person’s likeness or is a fully synthetic original.
- Attach the character’s generation record, including tool name, version, date, and prompt parameters, to the account file.
Risk Scenarios for Unverified Identities
Publishing AI-generated content under an unverified account creates one of the fastest paths to permanent termination. OpenAI holds the account owner responsible for all end-user generated content, and organizations using the API for content generators can lose entire accounts if users produce prohibited material. Subscription platforms apply the same accountability principle, so the verified account holder remains liable for every asset published under that account, regardless of which team member uploaded it.
Likeness-Ownership Documentation for AI Characters
Sub-Checklist for Likeness Rights
- For characters based on a real person, obtain and file a signed release that covers the specific platform, territory, duration, and content type.
- For fully synthetic characters, retain generation records that show the likeness was invented rather than derived from an identifiable individual.
- Define “digital replica” and “AI use” in all talent and vendor contracts with enough precision to separate routine editing from full synthetic recreation.
- Review all existing NIL agreements for AI-specific addenda before publishing AI-generated content that features any public figure or athlete.
Risk Scenarios for Likeness Misuse
Lathrop GPM recommends that commercial agencies prohibit feeding a person’s content, likeness, voice, or biometric identifiers into third-party or open-source AI tools without express consent and require vendors and agencies to follow the same restrictions. Omni Legal Group advises brands and marketing agencies to update vendor and technology contracts for AI-specific use cases and to conduct rights clearance reviews before publishing any AI-assisted creative content. Agencies that skip these steps expose themselves to publicity-rights claims, even for synthetic faces, if the generation process drew on identifiable source material.
Reusable-Asset Record-Keeping for Every Shoot
Sub-Checklist for Asset Records
- Log every reusable setting, outfit, and object with its creation date, tool version, and the character it is authorized for, which forms the base of your asset inventory.
- Store these asset records in a designated repository, not inside the AI generation tool, so records remain available if tools change or access is lost.
- Apply retention periods by asset type, using 30 to 90 days for raw generation logs that support operational review and 1 to 6 years for decision and approval records that support legal defense and audits.
- Maintain a separate record series that distinguishes AI-edited drafts from final published versions, since courts treat these as different record types with different discovery obligations.
Risk Scenarios for Missing Asset Histories
Reed Smith counsel Kiriaki Tourikis and Craig W. Chaney warn that organizations adopting AI tools without updating records and information management frameworks create governance gaps that expose them to spoliation, discovery failures, and compliance risks, because courts treat AI-generated content, including prompts, as discoverable. Practical data traceability methods include creating separate record series for AI-edited drafts and final versions, retaining metadata used during generation to preserve audit trails, and requiring signatures or logs for any changes to AI records.
Sozee’s Vault stores every image, video, voice note, and Live Mode snap in creator-controlled folders, with asset lineage preserved from creation through publication. Every reusable setting, outfit, and object is saved as a named asset, not a re-entered prompt, so the record exists by default.
Multi-Character Workspace Isolation for Agencies
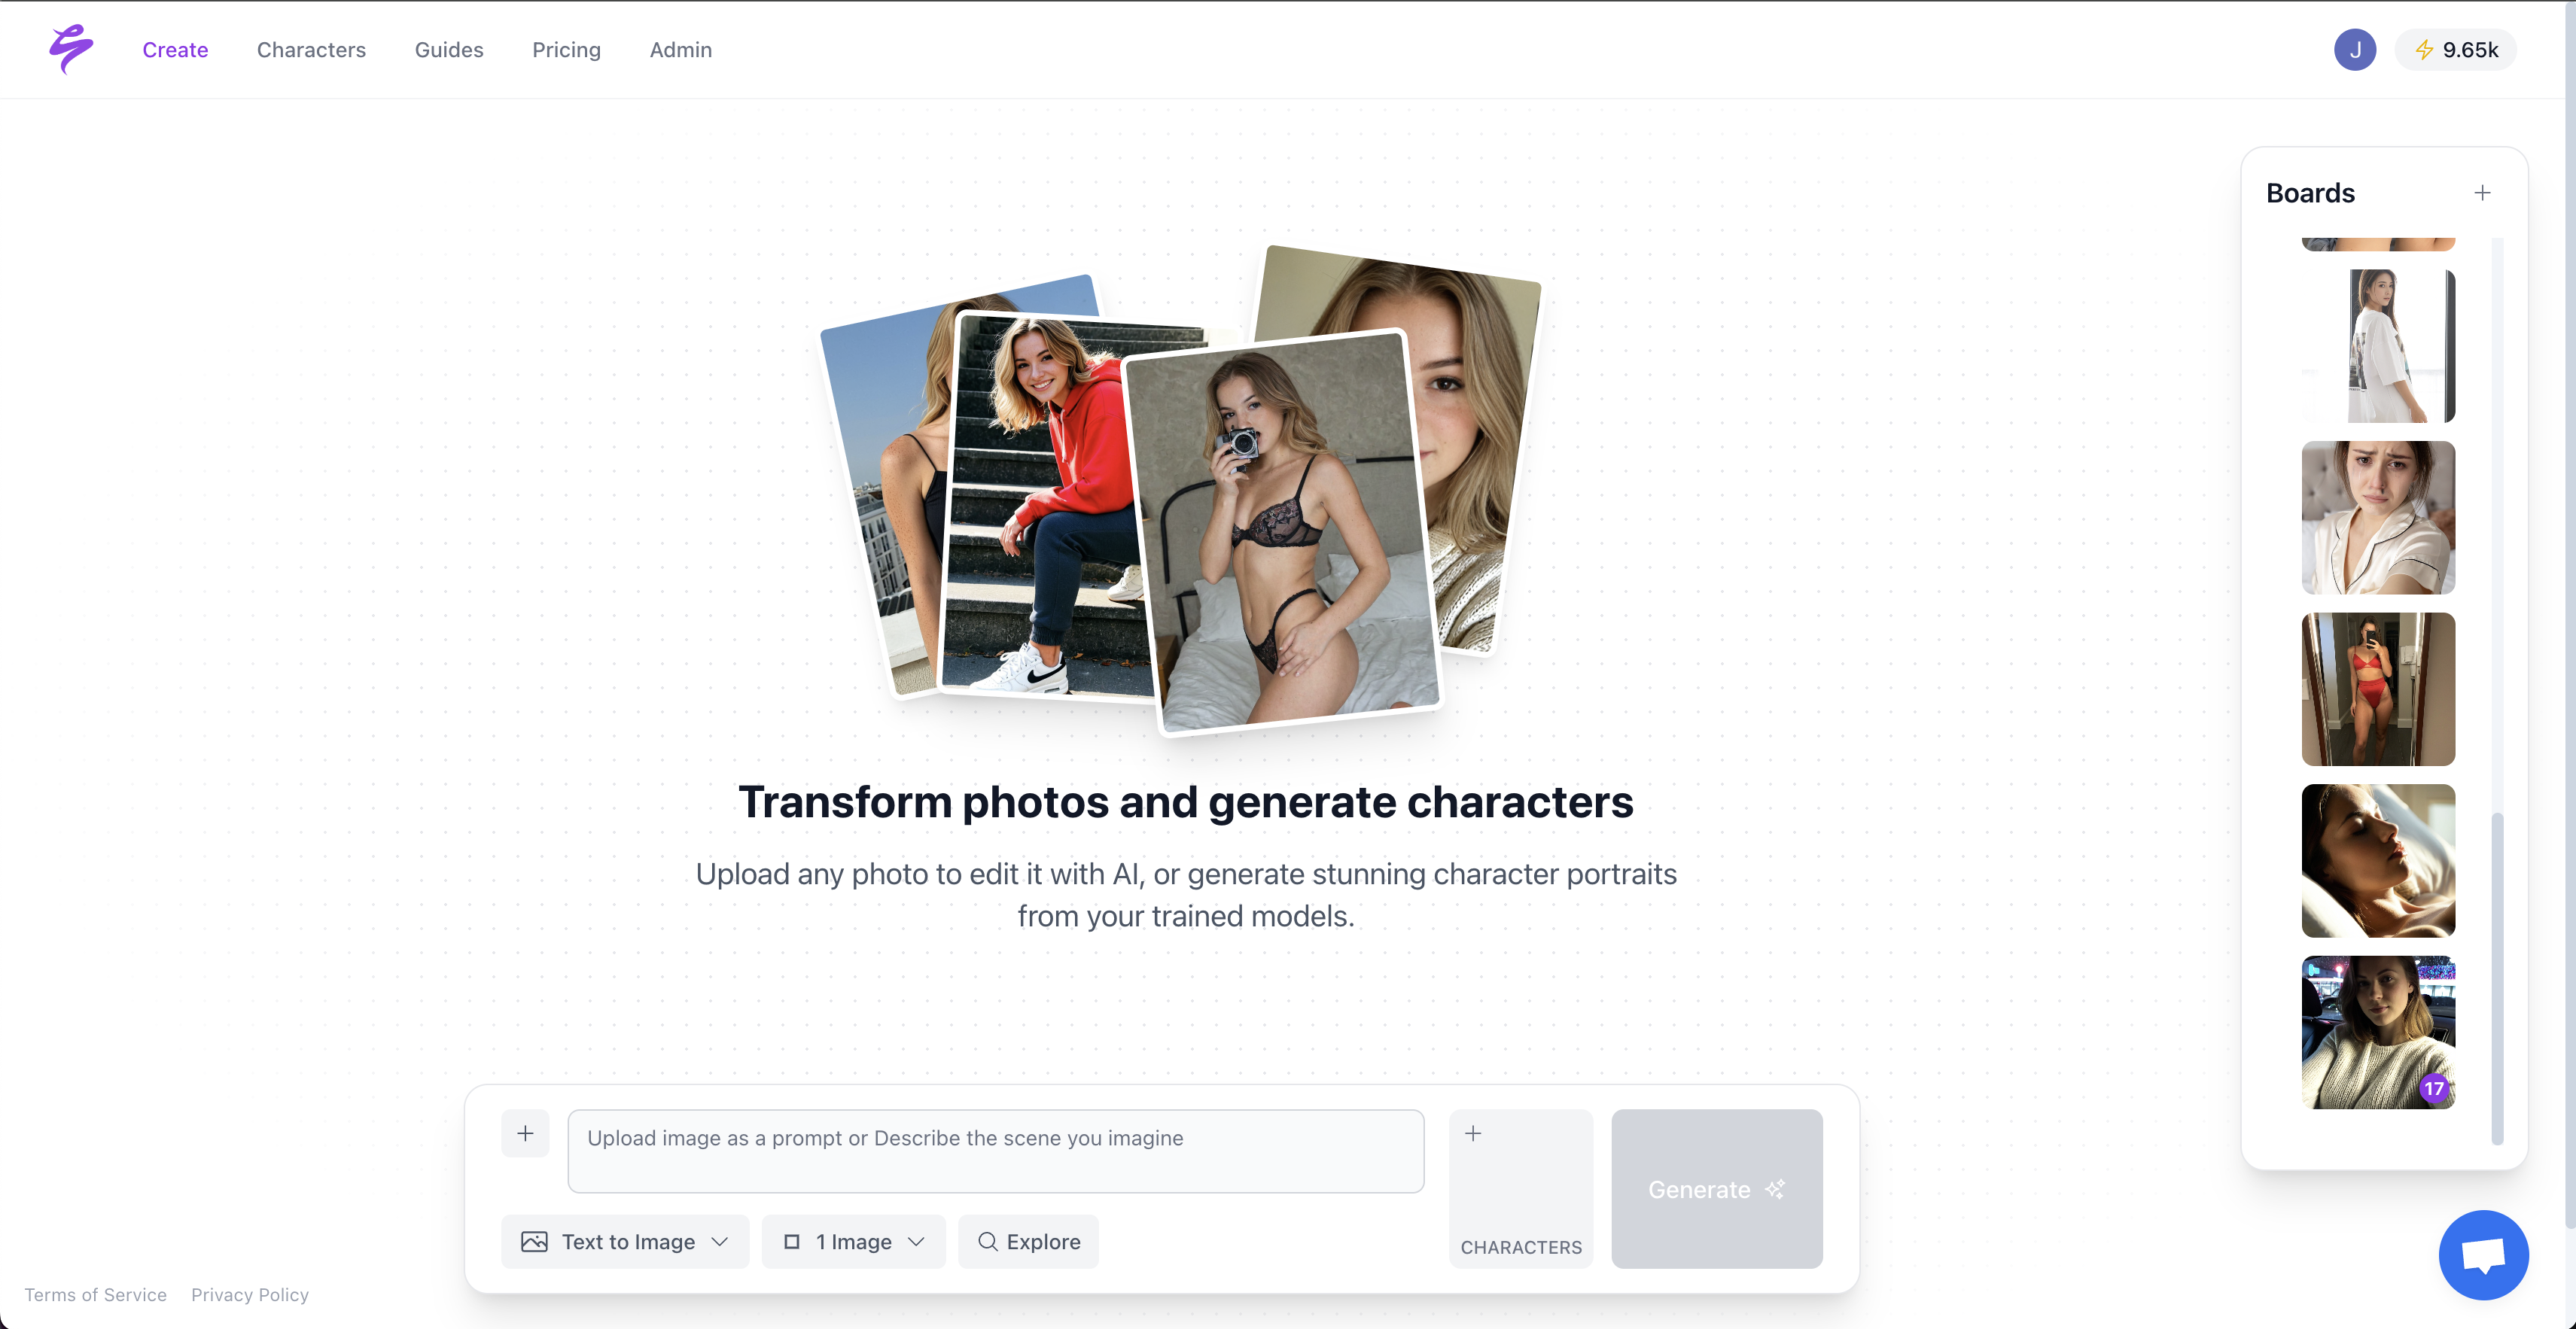
Sub-Checklist for Workspace Boundaries
- Assign each creator character to a fully isolated workspace with its own vault, connected accounts, and credit pool, which sets the isolation boundary.
- Prohibit cross-character asset sharing unless a formal transfer log is created and approved, which prevents the most common source of cross-contamination.
- Assign a named operator to each workspace and log all access events, which creates accountability for every action inside that boundary.
- Apply role-based access control so team members can only access the workspaces they are authorized for, which enforces isolation at the authentication layer instead of relying on operator discipline.
Risk Scenarios for Cross-Character Contamination
A preflight checklist for reducing ban risk requires each account to have a named owner and operator list, an assigned browser profile or cloud phone workspace, review requirements for sensitive actions, and a pause rule triggered by warnings or unclear ownership. Recommended isolation boundaries for AI memory include hard tenant isolation, separate namespaces or permission filters per customer or account, and role-specific retrieval unless shared source is explicitly approved.
Sozee’s Teams and Workspaces feature gives agencies one login with every client fully isolated, and each workspace has its own characters, vault, connected accounts, and credits. Cross-character contamination becomes structurally blocked instead of controlled only by policy.
SFW-to-NSFW Ramp Controls and Content Ceilings
Sub-Checklist for Content Tiers
- Set the content ceiling for each character explicitly before any shoot begins, not after images or clips exist.
- Confirm the account tier and platform permissions match the content ceiling assigned to that character.
- Document the SFW-to-NSFW arc for each Photo Shoot set, including which frames belong to which distribution tier.
- Apply EU AI Act Article 50 labeling requirements, using digitally-signed metadata and imperceptible watermarking on every frame as the asset is created, not only at upload.
Risk Scenarios for Misaligned Content Tiers
AI-generated or manipulated images, audio, and video that qualify as deepfakes or synthetic media must carry clear labeling as artificially generated, with machine-readable provenance metadata that survives reformatting, localization, and reuse across channels. Uploading NSFW AI content without embedded provenance metadata creates a compliance failure under both platform policy and EU law for any agency with European subscribers. Sozee’s Photo Shoot feature sets the SFW-to-NSFW ramp and ceiling during shoot setup, which turns the content tier into a deliberate choice instead of a rushed post-generation review.
Agent-Assisted Shoot Audit Trails for Every Asset
Sub-Checklist for Audit Logging
- Log the exact prompt, system instructions, generation parameters, model name, and model version for every asset produced.
- Record every human edit, approval, and operator action with a timestamp and user ID.
- Store audit logs in tamper-proof or write-once storage, not in the generation tool’s default cache.
- Retain decision and action histories for 1 to 6 years to support audits, dispute resolution, and regulated-services requirements.
Risk Scenarios for Missing Audit Trails
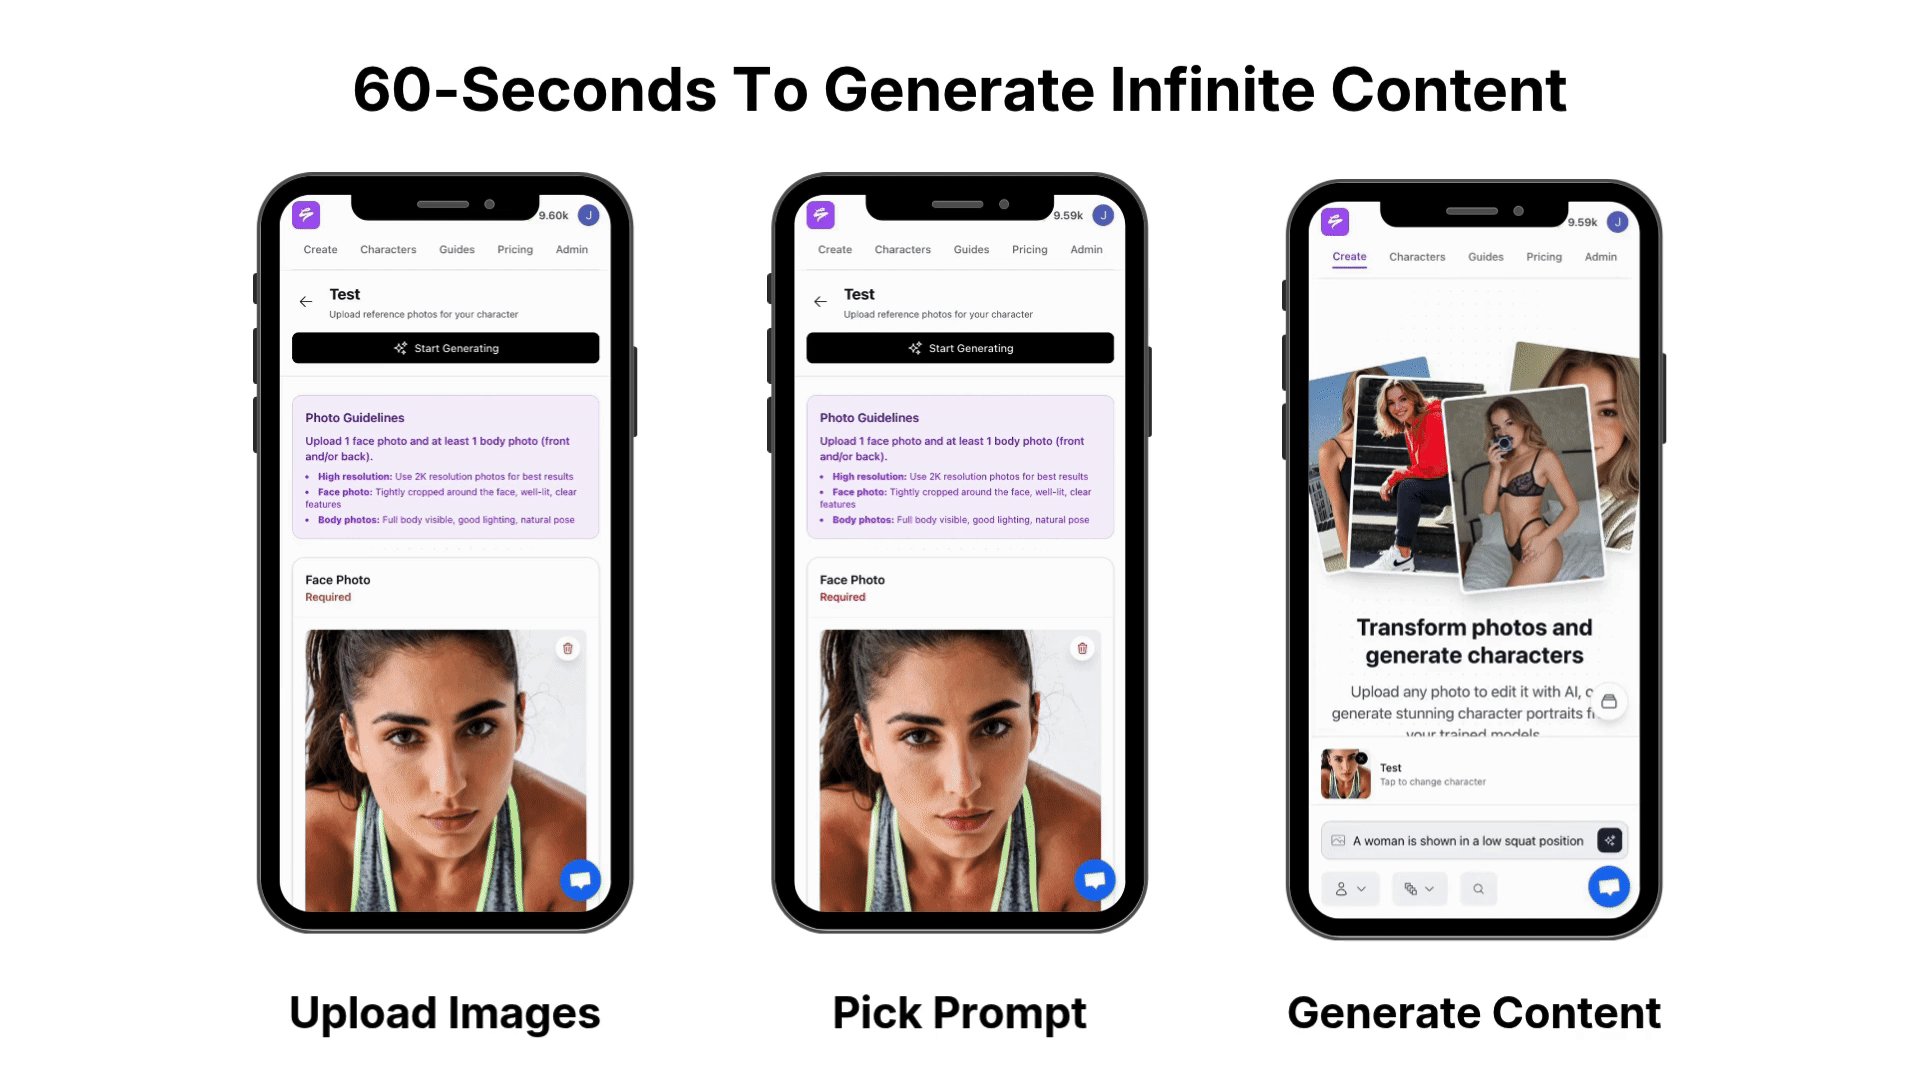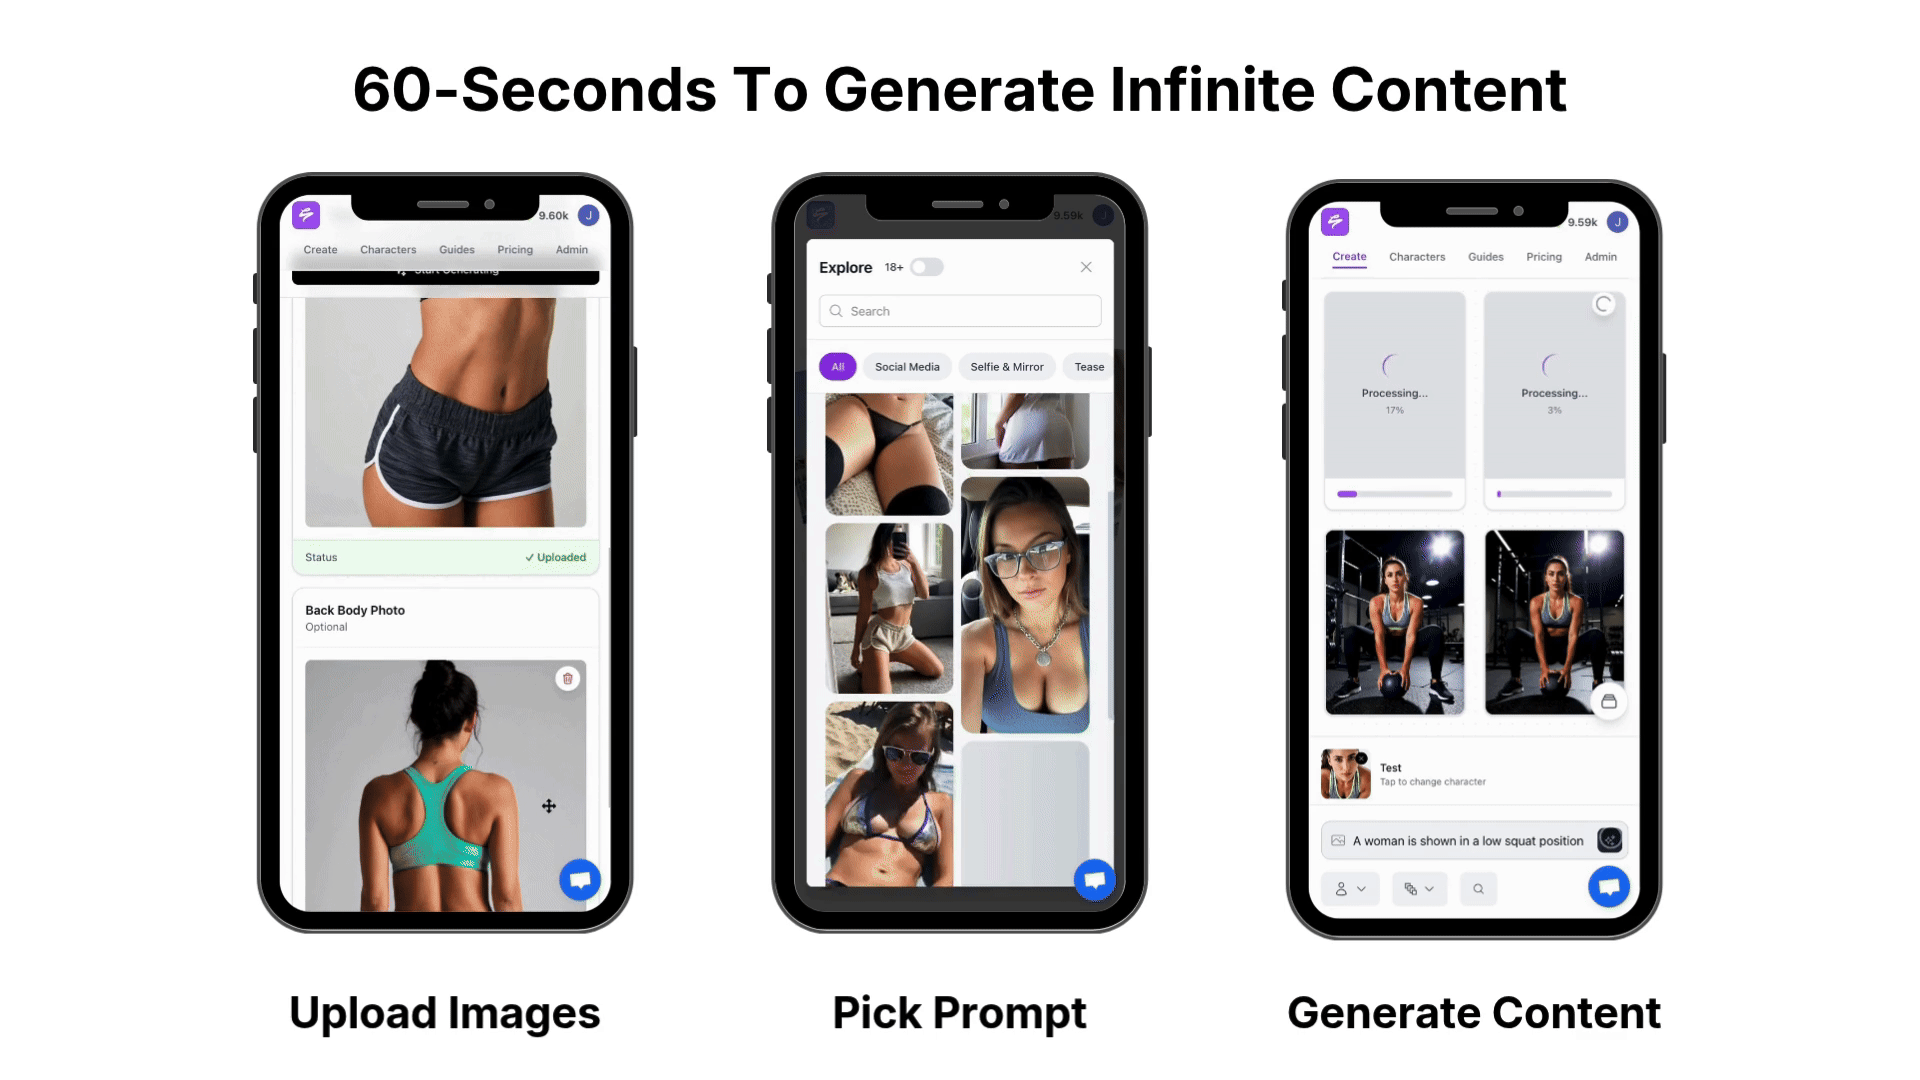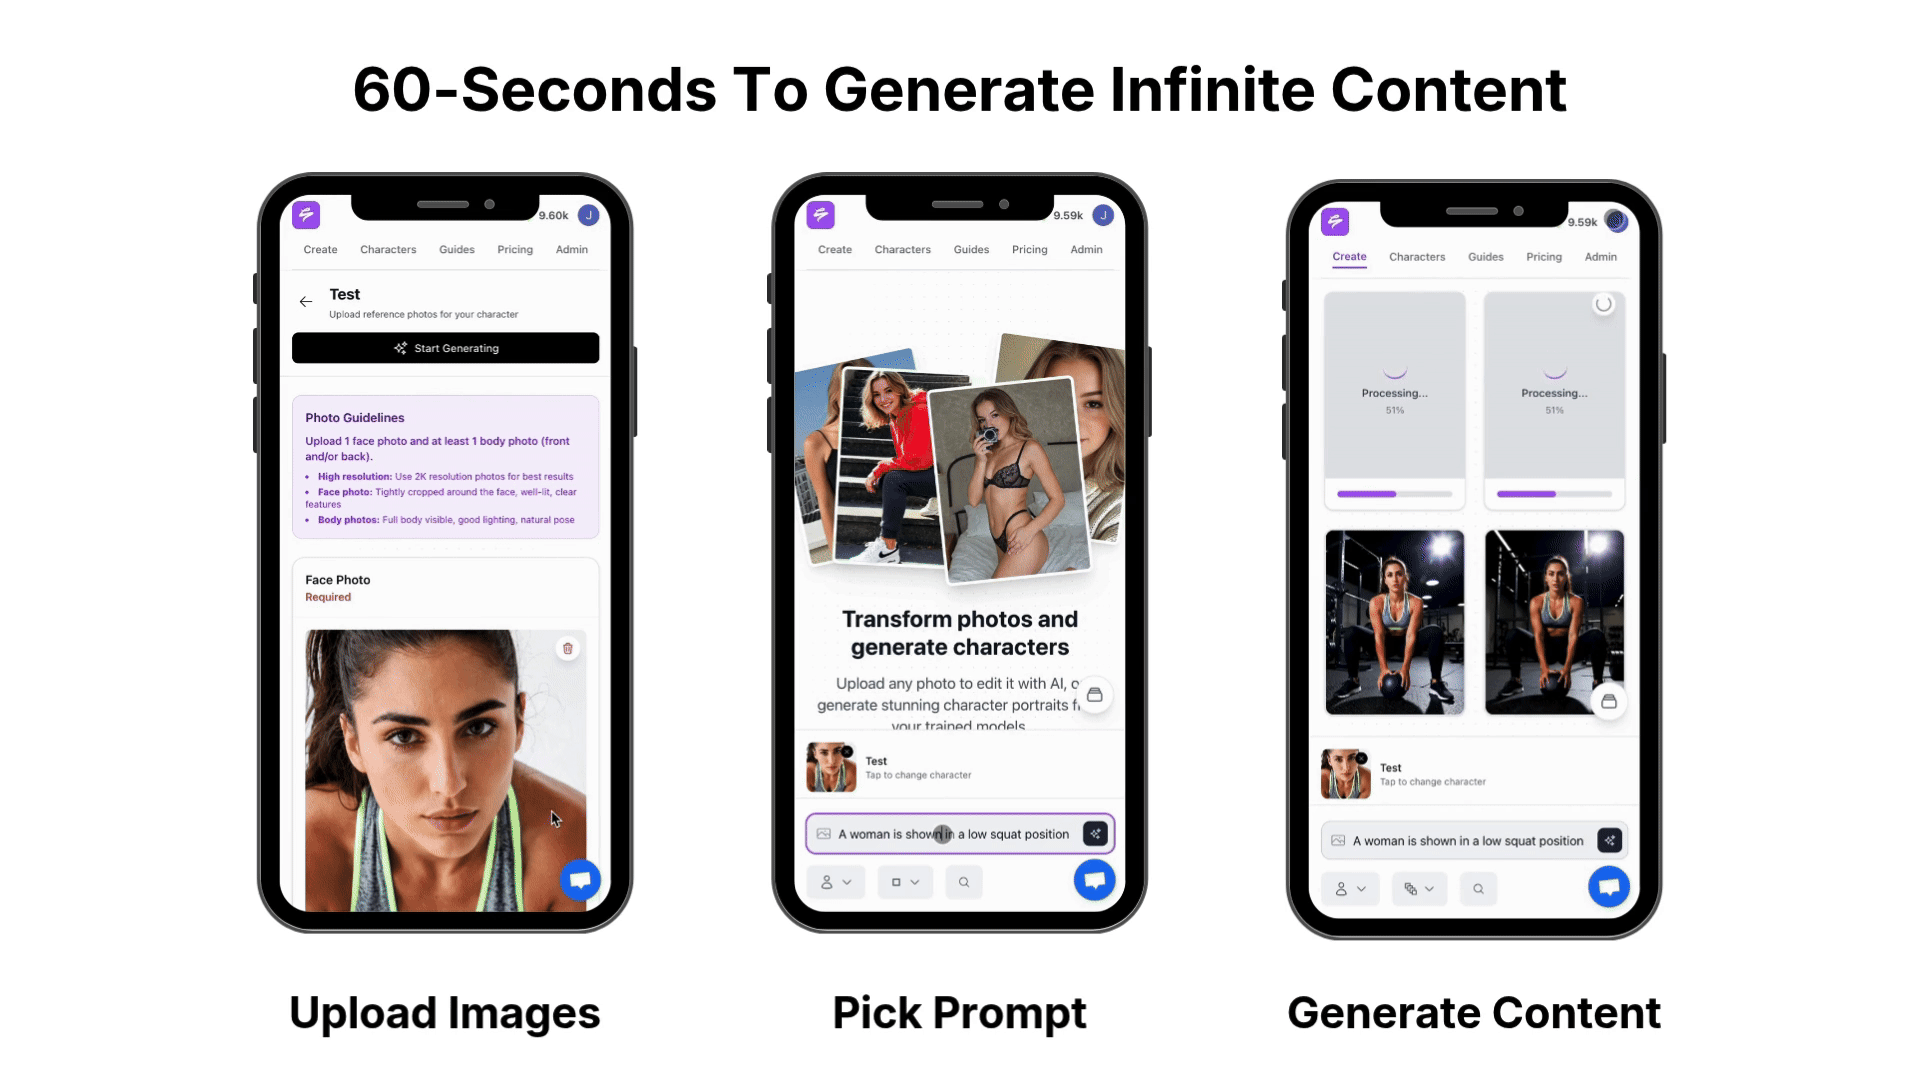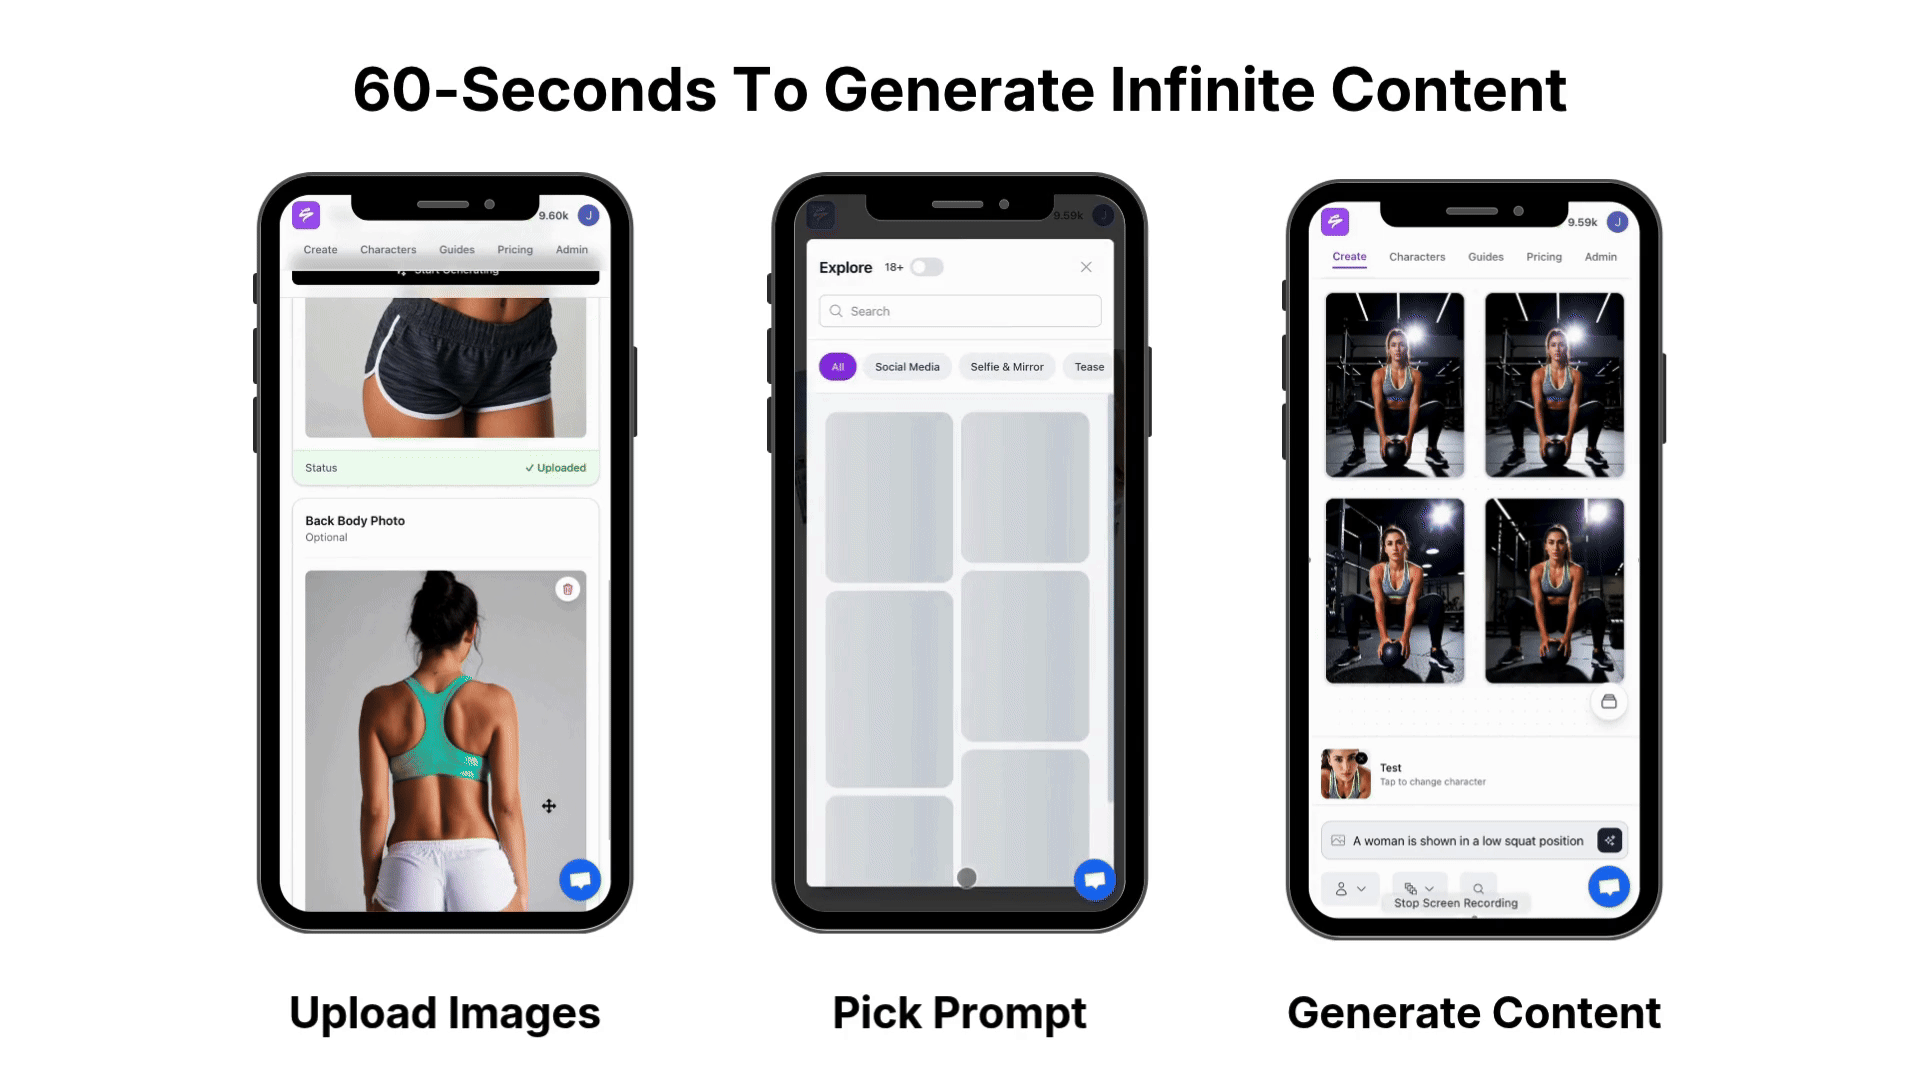
An AI content audit trail is an immutable, chronological record of every action and decision in the AI content lifecycle, including the exact prompt, system instructions, generation parameters, model version and provider, source data, and all human edits and approvals. In the OpenAI copyright litigation, Magistrate Judge Ona T. Wang directed OpenAI to preserve and segregate output log data that otherwise would have been deleted, including data subject to user deletion requests or ordinary deletion practices, which confirms that AI output logs are discoverable and must be preserved proactively. Sozee’s Agent writes directly into the prompt bar and Photo Control panel, creating a native record of every shoot setup decision before any pixels are generated.
Post-Upload Monitoring and Rollback Procedures
Sub-Checklist for Live Content Oversight
- Monitor each published asset for platform enforcement flags within 24 hours of upload.
- Maintain a rollback log that tracks which assets are live, which are under review, and which have been removed.
- Pause all uploads from the affected workspace immediately if a warning arrives, then run a full audit before resuming.
- Document every remediation step and store that record alongside the original audit trail.
Risk Scenarios for Ignoring Enforcement Signals
Recommended mitigations for preserving account integrity include dedicated workspaces or devices, explicit role assignment, content review notes, task logging, and recovery checklists before scaling operations. The EU AI Act requires deployers to retain automatic event logs for at least six months under Article 26, unless other EU or national law requires a longer period. Post-upload monitoring becomes a minimum legal requirement for agencies that distribute into regulated markets, not an optional safeguard.
Why Tool-Embedded Verification Beats Manual Disclosure
Manual caption disclosure relies on creators adding text labels after generation. This method creates no audit trail by default and needs a separate logging workflow. Because disclosure depends on individual operator discipline, the majority of creators skip it, as shown in the problem section’s data.
Platform-native tagging uses a manual tag at upload but does not embed metadata during creation. The resulting log lives only inside the platform and cannot be exported for legal defense. Each upload requires a manual tagging step, and the platform does not provide workspace isolation to prevent cross-character contamination.
Standalone EU AI Act watermarking applies digitally-signed metadata and imperceptible watermarking while the asset is created. Correct implementation keeps metadata intact through reformatting, although a separate audit log is still needed for human approvals. This approach also requires integration with the generation tool, which often lacks a native agency workflow.
Sozee’s tool-embedded verification records likeness lock, character registration, and shoot parameters during setup, before any generation runs. The Agent writes shoot setup into the prompt bar and Photo Control panel, the Vault stores full asset lineage, and workspace logs capture every operator action. Teams and Workspaces isolate each creator so one login can manage a full roster while still maintaining per-character audit trails.
Frequently Asked Questions
How do agencies verify that AI-generated content meets OnlyFans policy requirements before uploading?
Verification requires a pre-upload process that checks four specific items. The account must be identity-verified and the AI character must be registered with a named human owner. The likeness used must either be covered by a signed release or documented as a fully synthetic original. The content tier must match the account’s platform permissions. The asset must carry embedded provenance metadata created during generation, not added later. Manual caption disclosure alone cannot satisfy these requirements at agency scale. A tool-embedded workflow, where character registration, shoot parameters, and asset records are created before generation starts, is the only approach that produces a defensible audit trail across a multi-creator roster.
What records does an OnlyFans agency need to keep for AI-generated content, and for how long?
Record-keeping requirements depend on record type. Raw generation logs, including prompts, parameters, and model versions, warrant 30 to 90 days for service review and complaint handling. Decision and approval records, including human edits, operator actions, and content-ceiling assignments, warrant 1 to 6 years to support audits and dispute resolution. Likeness-ownership documentation, such as signed releases, synthetic-character generation records, and NIL agreement addenda, should be retained for the full duration of the content’s commercial use plus any applicable statute of limitations. All records should live in a designated repository outside the AI generation tool, with tamper-proof or write-once storage for audit logs. Agencies that distribute into EU markets must also retain automatic event logs for at least six months under EU AI Act Article 26.
What are the specific risks of using synthetic identities on OnlyFans, and how does workspace isolation reduce them?
Synthetic identities create two main risk categories. The first involves platform enforcement, because content published under an unverified account or without a registered human owner of record violates policy and can trigger immediate termination. The second involves legal exposure, because a synthetic face that was generated using identifiable source material, even by accident, can create publicity-rights claims under statutes such as California Civil Code Section 3344. Workspace isolation reduces both risks by keeping each AI character in a fully separated environment with its own vault, connected accounts, and operator log. Cross-character asset contamination, where a setting or outfit built for one character is reused for another without documentation, remains one of the most common compliance failures in multi-creator agencies. Hard workspace isolation makes that contamination structurally impossible instead of relying on policy reminders.
Does the EU AI Act apply to OnlyFans agencies, and what does compliance require in practice?
The EU AI Act’s Article 50 transparency requirements apply to any agency that deploys generative AI systems to produce content that reaches EU subscribers, regardless of the agency’s location. From 2 August 2026, Article 50’s metadata and watermarking requirements, described in the SFW-to-NSFW section above, must be applied during generation, not at upload and not through manual captions. Agencies must also ensure that provenance metadata stays attached through reformatting and reuse across channels. In practice, compliance requires a generation tool that embeds metadata natively, a human-approval log for every published asset, and event logs retained for at least six months. Agencies that rely only on manual disclosure workflows or platform-native tagging are not compliant with Article 50 as of August 2026.
Conclusion: Build a Compliance-Native AI Studio
The 2026 compliance environment for OnlyFans AI-generated content creates a workflow challenge, not a policy-summary challenge. Agencies that treat disclosure as a manual step, record-keeping as an afterthought, and workspace isolation as optional will keep losing accounts at scale. The 7-step checklist in this playbook connects every material compliance requirement to a specific production control. Sozee embeds those controls into the cast, direct, and create workflow so compliance becomes the default output of every shoot, not a separate review process bolted on afterward.
Locked likeness, isolated workspaces, agent-assisted audit trails, native SFW-to-NSFW ramp controls, and a Vault that preserves full asset lineage from creation through publication together form the architecture of a studio built to scale AI content without losing accounts.